admin
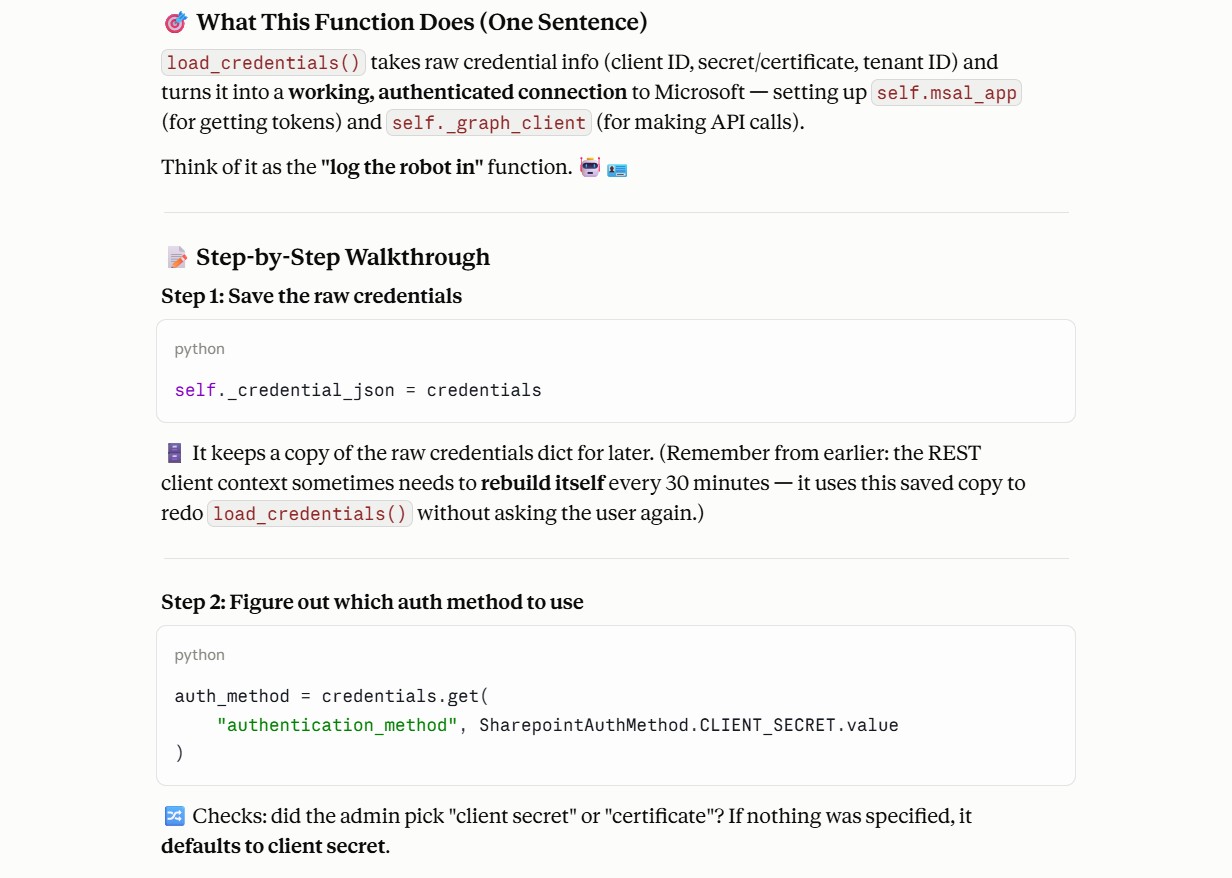
def load_credentials(self, credentials: dict[str, Any]) -> dict[str, Any] | None:
        self._credential_json = credentials
        auth_method = credentials.get(
            "authentication_method", SharepointAuthMethod.CLIENT_SECRET.value
        )
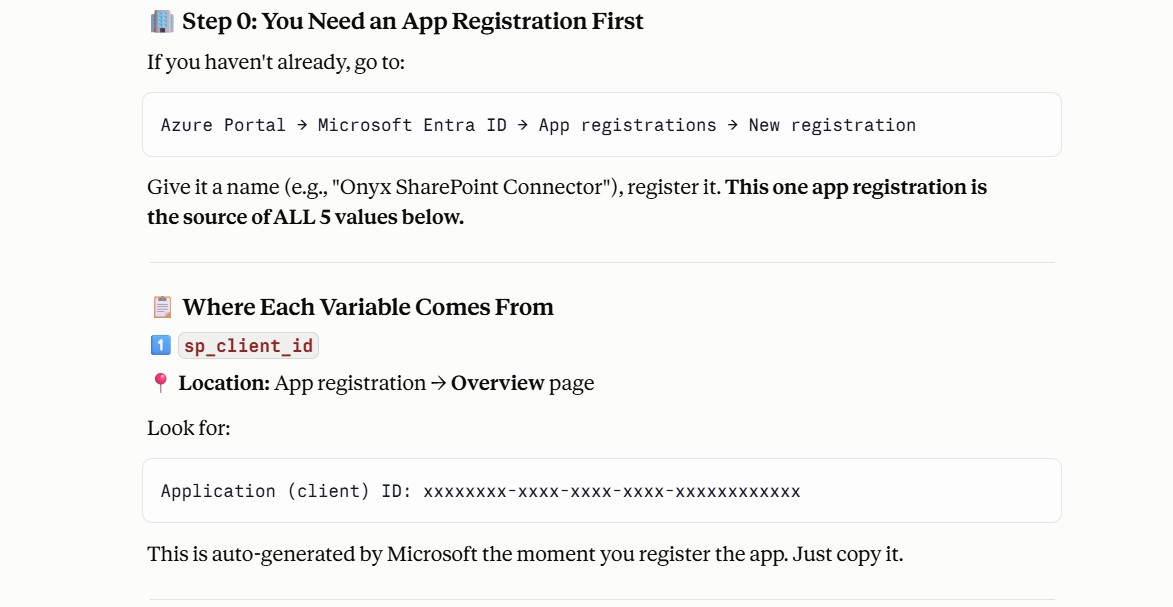
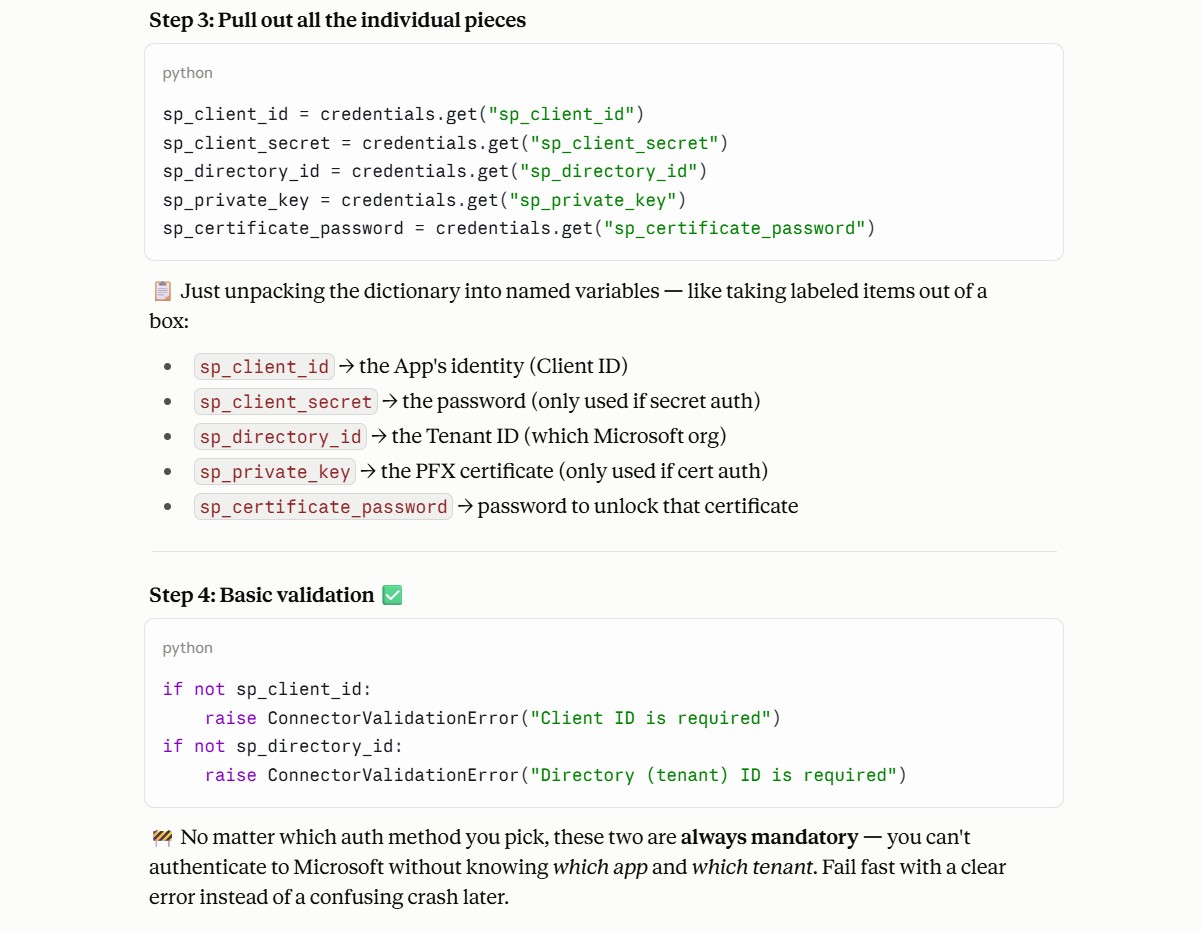
        sp_client_id = credentials.get("sp_client_id")
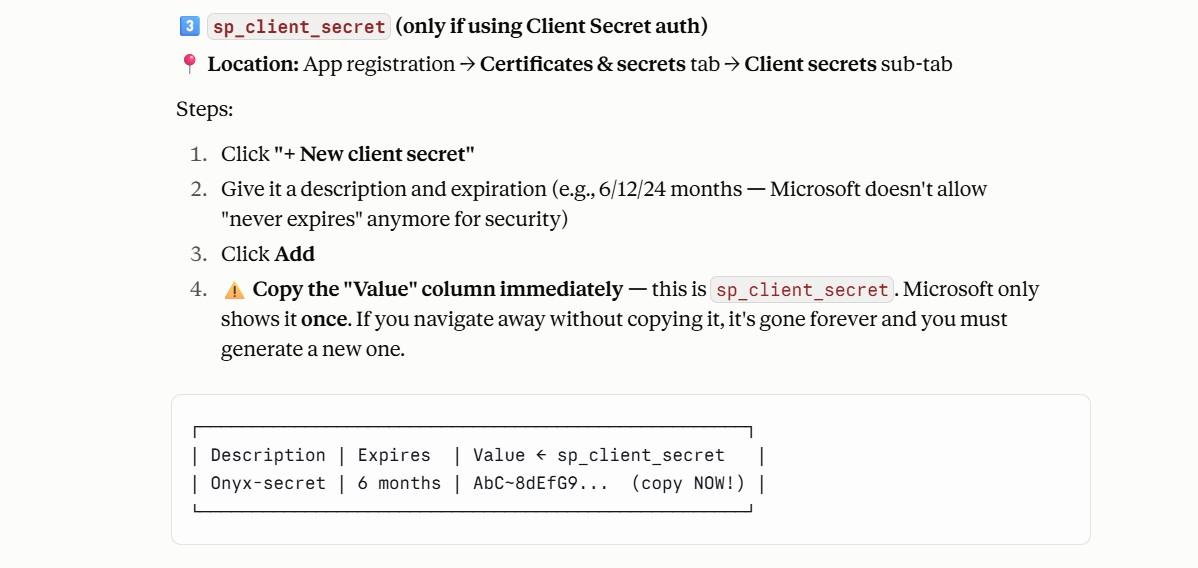
        sp_client_secret = credentials.get("sp_client_secret")
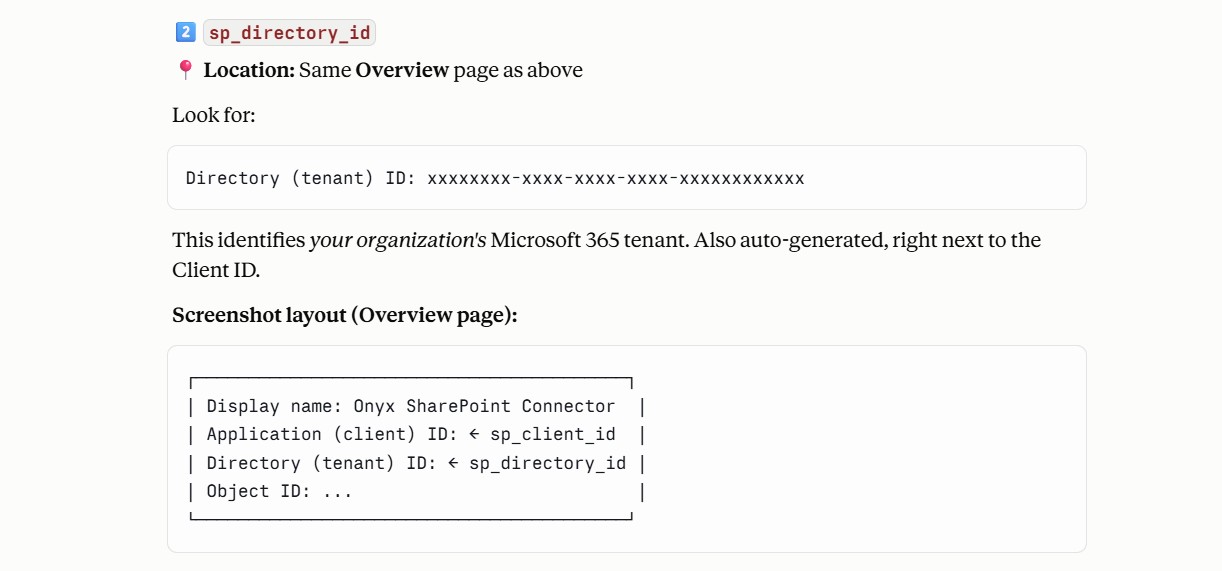
        sp_directory_id = credentials.get("sp_directory_id")
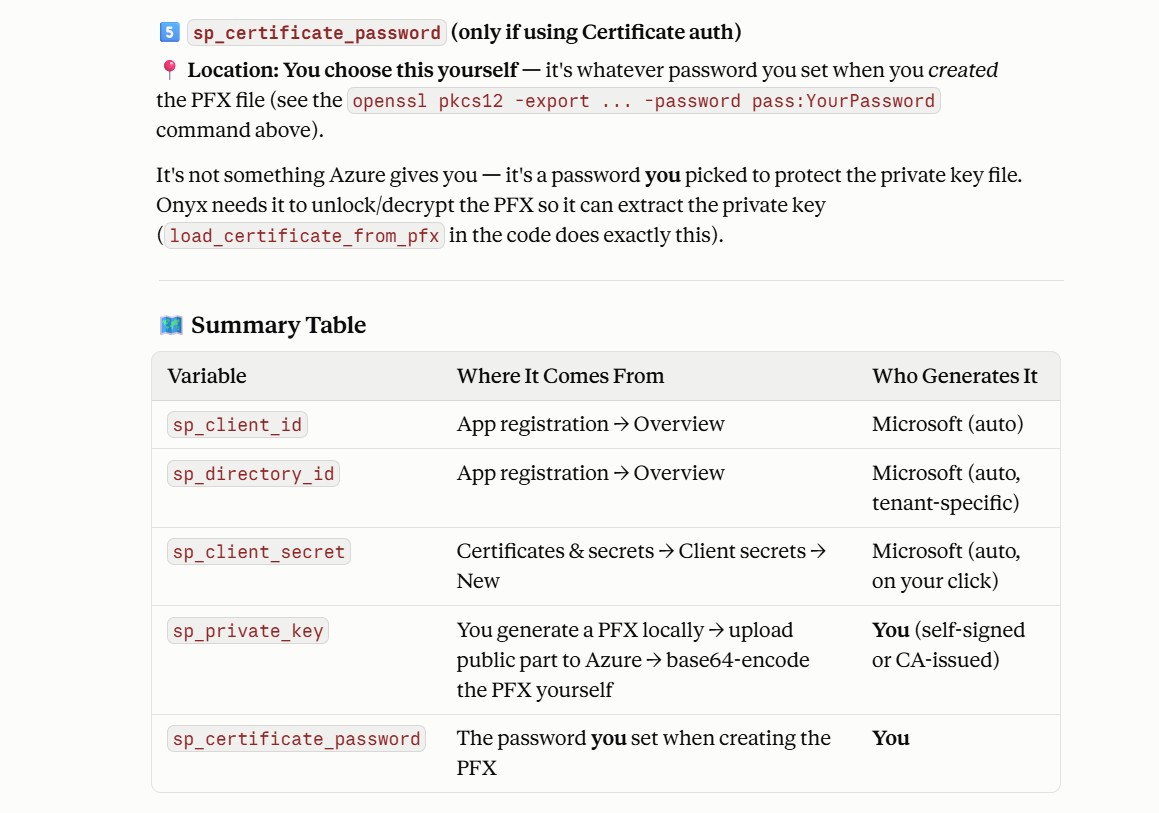
        sp_private_key = credentials.get("sp_private_key")
        sp_certificate_password = credentials.get("sp_certificate_password")

        if not sp_client_id:
            raise ConnectorValidationError("Client ID is required")
        if not sp_directory_id:
            raise ConnectorValidationError("Directory (tenant) ID is required")

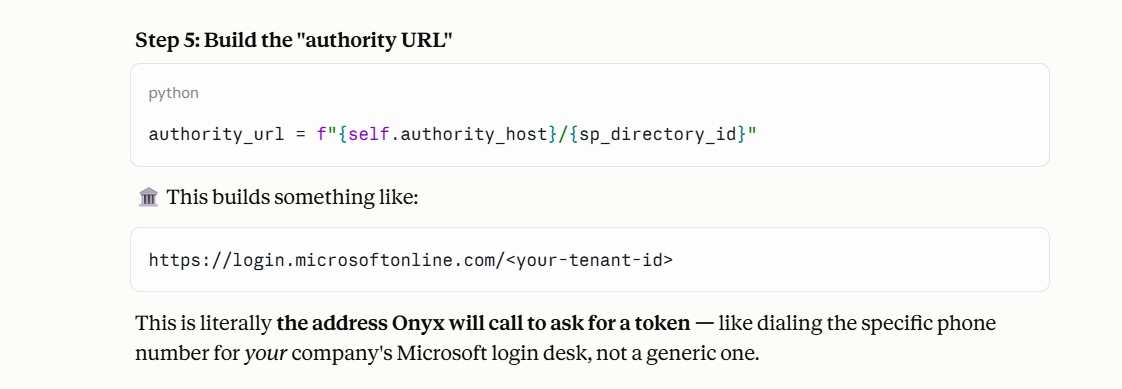
        authority_url = f"{self.authority_host}/{sp_directory_id}"

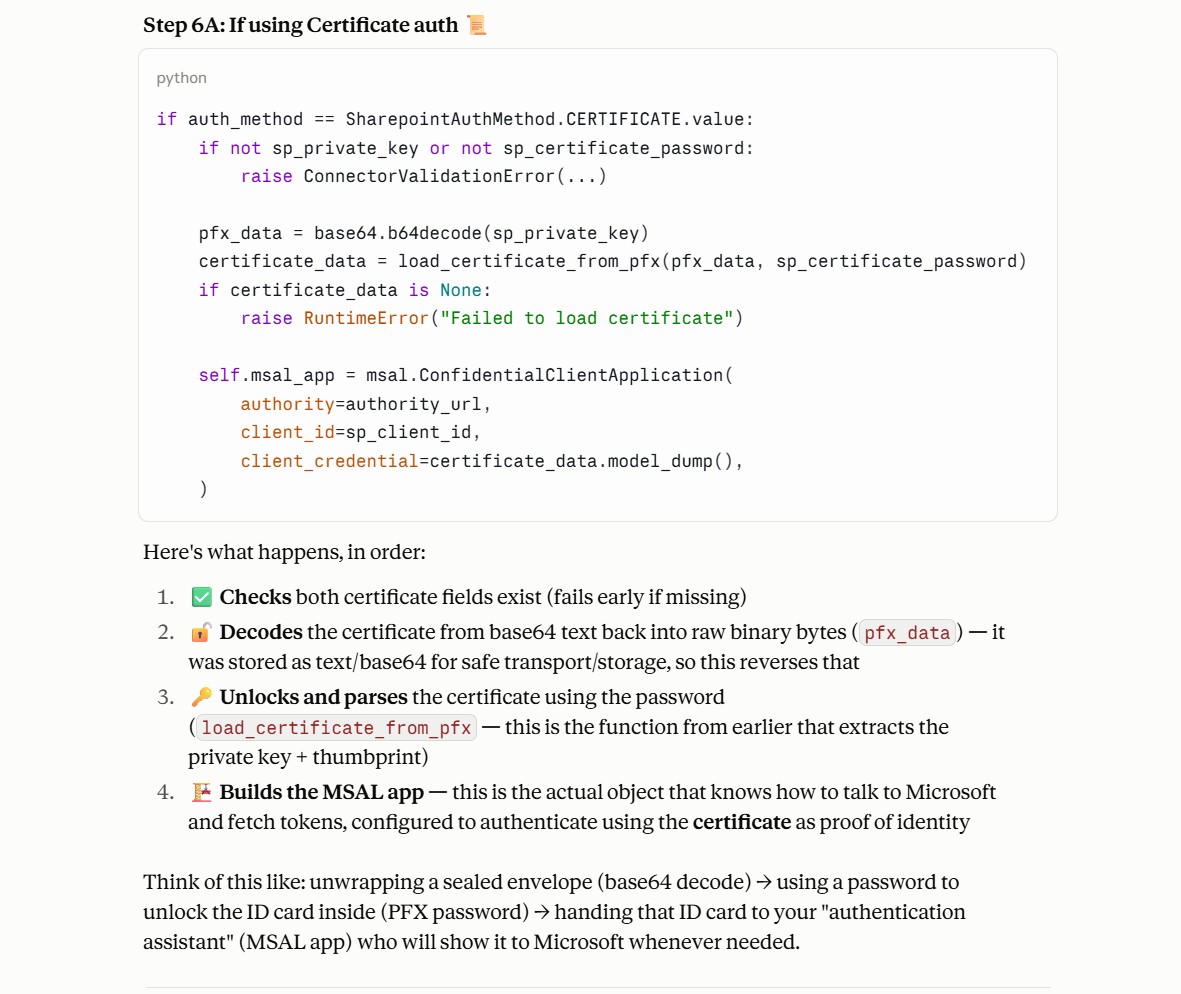
        if auth_method == SharepointAuthMethod.CERTIFICATE.value:
            logger.info("Using certificate authentication")
            if not sp_private_key or not sp_certificate_password:
                raise ConnectorValidationError(
                    "Private key and certificate password are required for certificate authentication"
                )

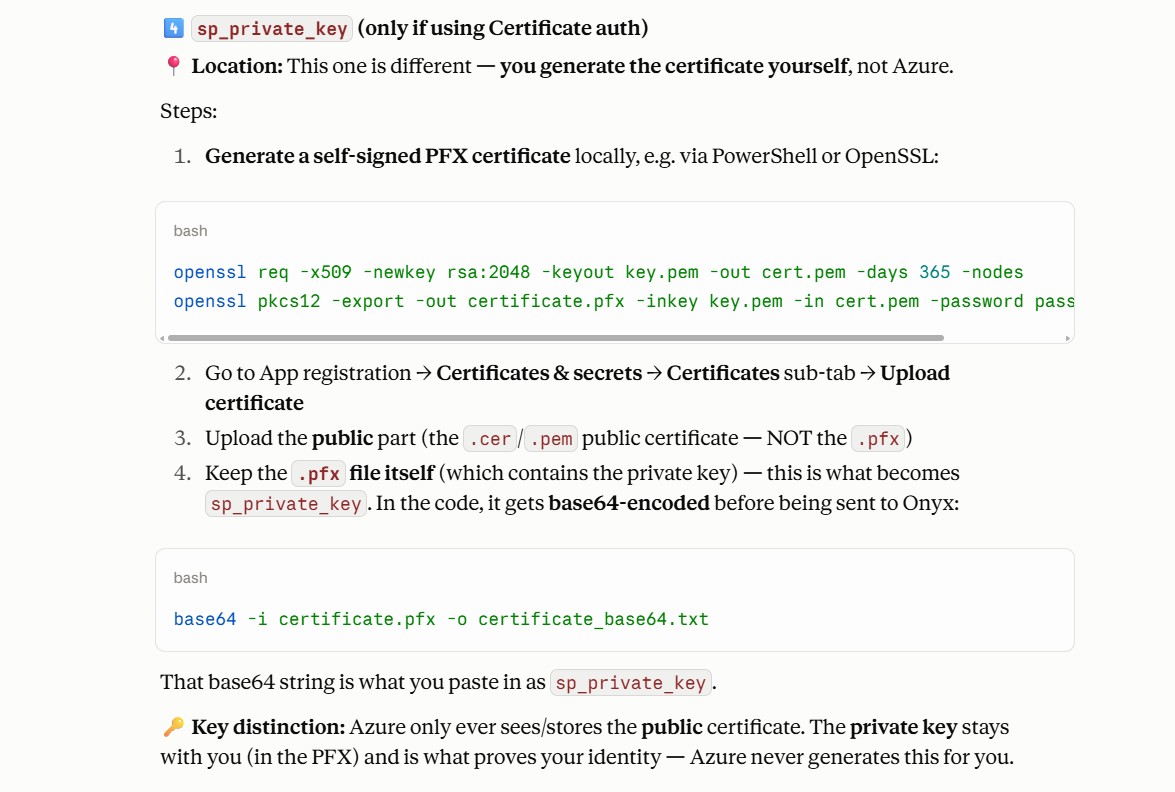
            pfx_data = base64.b64decode(sp_private_key)
            certificate_data = load_certificate_from_pfx(
                pfx_data, sp_certificate_password
            )
            if certificate_data is None:
                raise RuntimeError("Failed to load certificate")

            logger.info("Creating MSAL app with authority url %s", authority_url)
            self.msal_app = msal.ConfidentialClientApplication(
                authority=authority_url,
                client_id=sp_client_id,
                client_credential=certificate_data.model_dump(),
            )
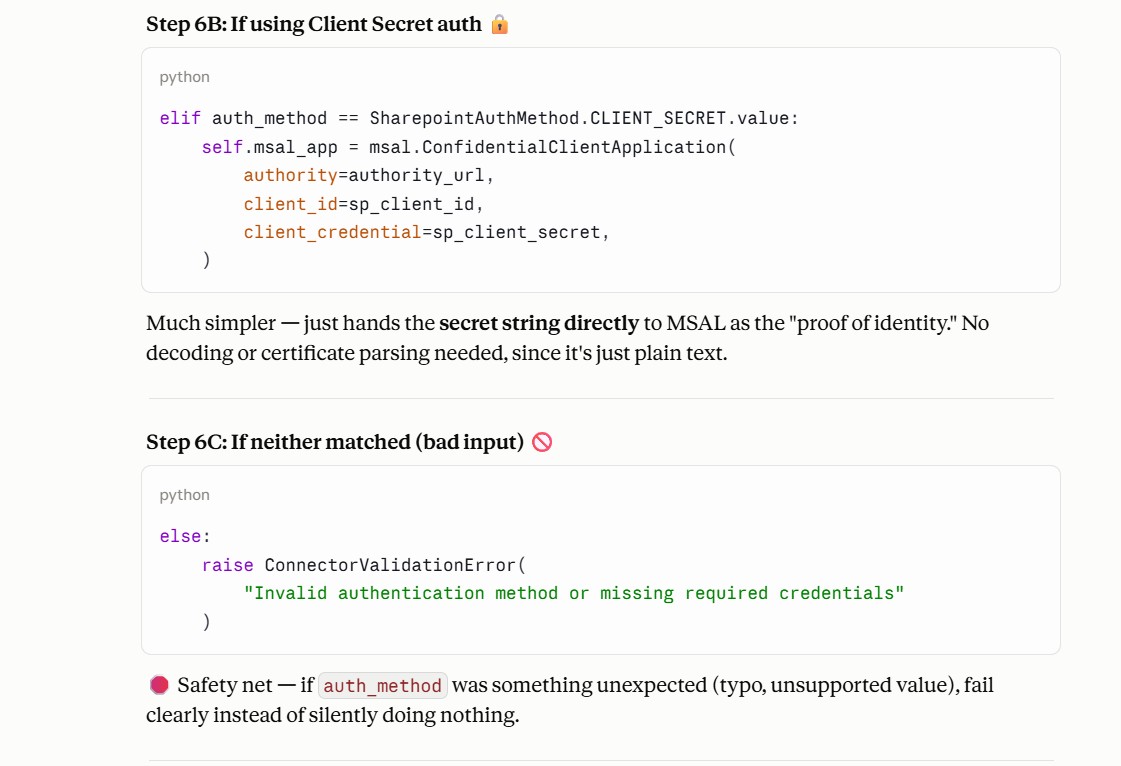
        elif auth_method == SharepointAuthMethod.CLIENT_SECRET.value:
            logger.info("Using client secret authentication")
            self.msal_app = msal.ConfidentialClientApplication(
                authority=authority_url,
                client_id=sp_client_id,
                client_credential=sp_client_secret,
            )
        else:
            raise ConnectorValidationError(
                "Invalid authentication method or missing required credentials"
            )

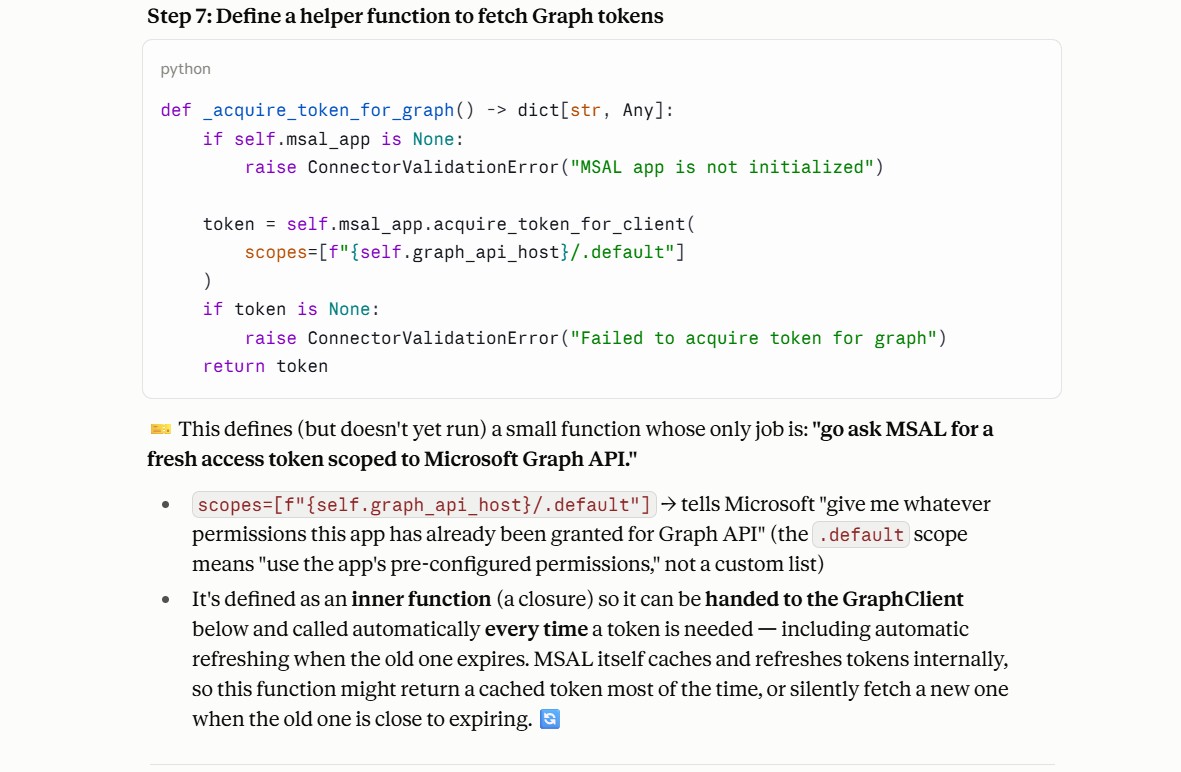
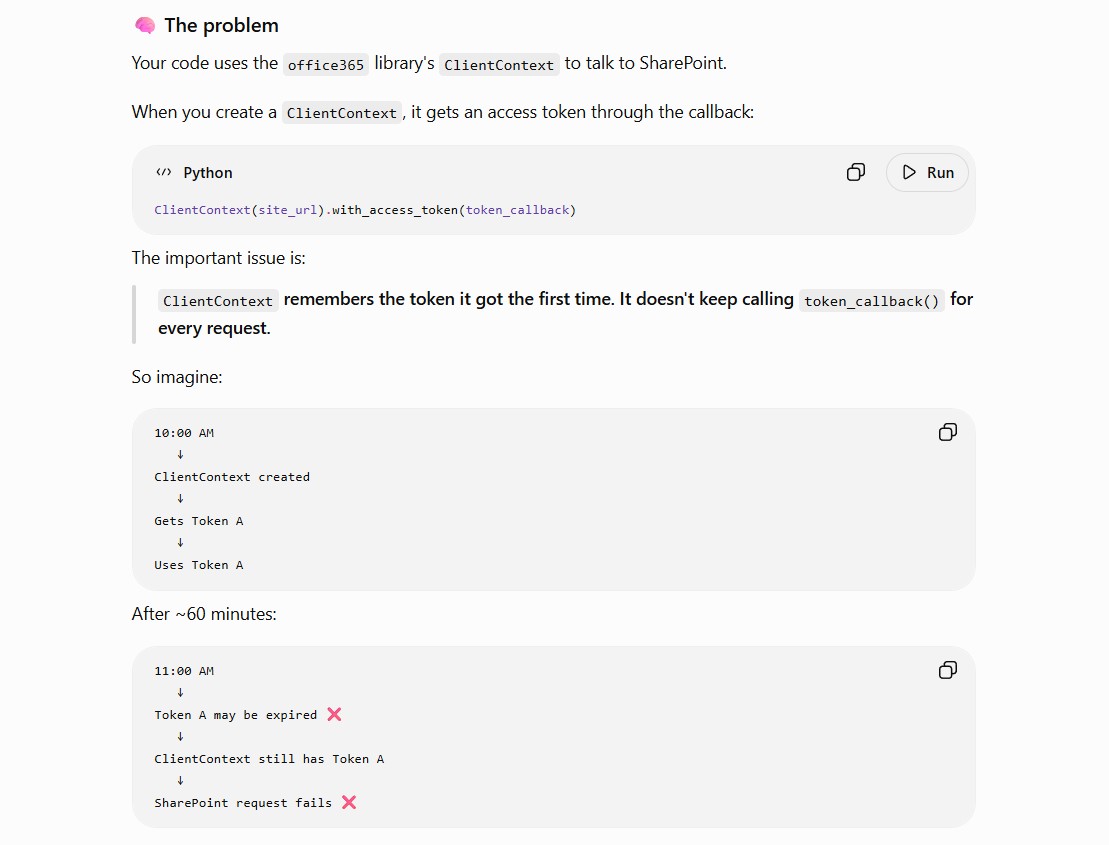
        def _acquire_token_for_graph() -> dict[str, Any]:
            """
            Acquire token via MSAL
            """
            if self.msal_app is None:
                raise ConnectorValidationError("MSAL app is not initialized")

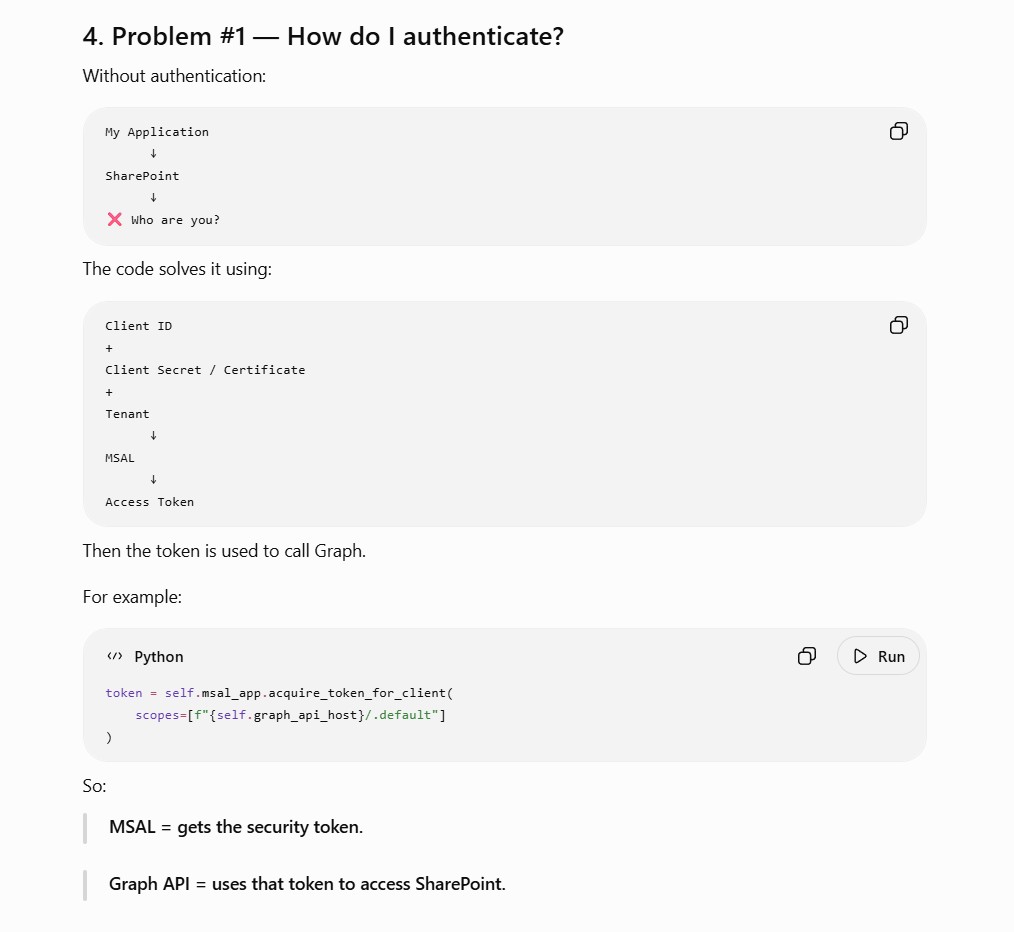
            token = self.msal_app.acquire_token_for_client(
                scopes=[f"{self.graph_api_host}/.default"]
            )
            if token is None:
                raise ConnectorValidationError("Failed to acquire token for graph")
            return token

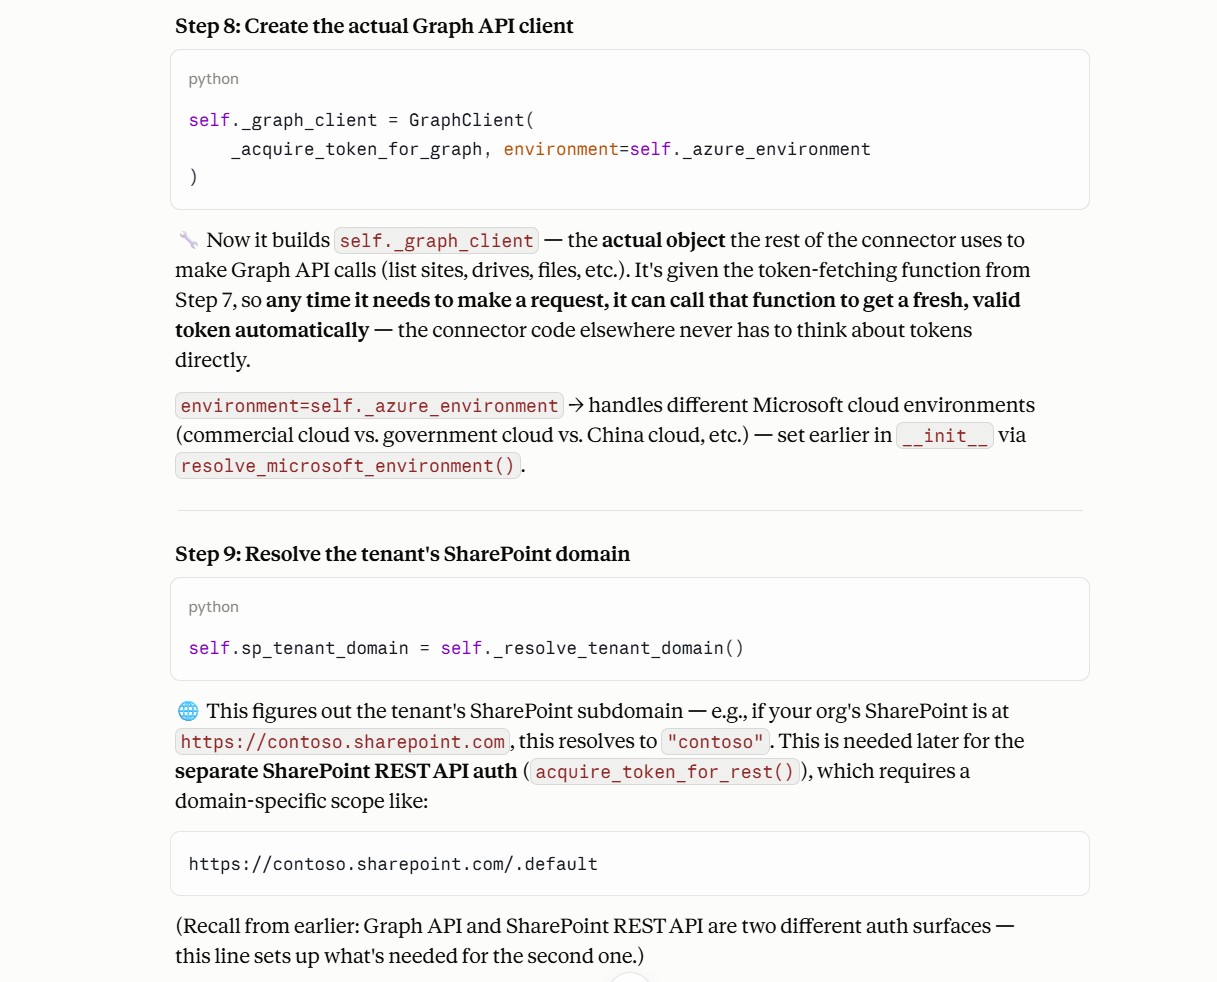
        self._graph_client = GraphClient(
            _acquire_token_for_graph, environment=self._azure_environment
        )
        self.sp_tenant_domain = self._resolve_tenant_domain()
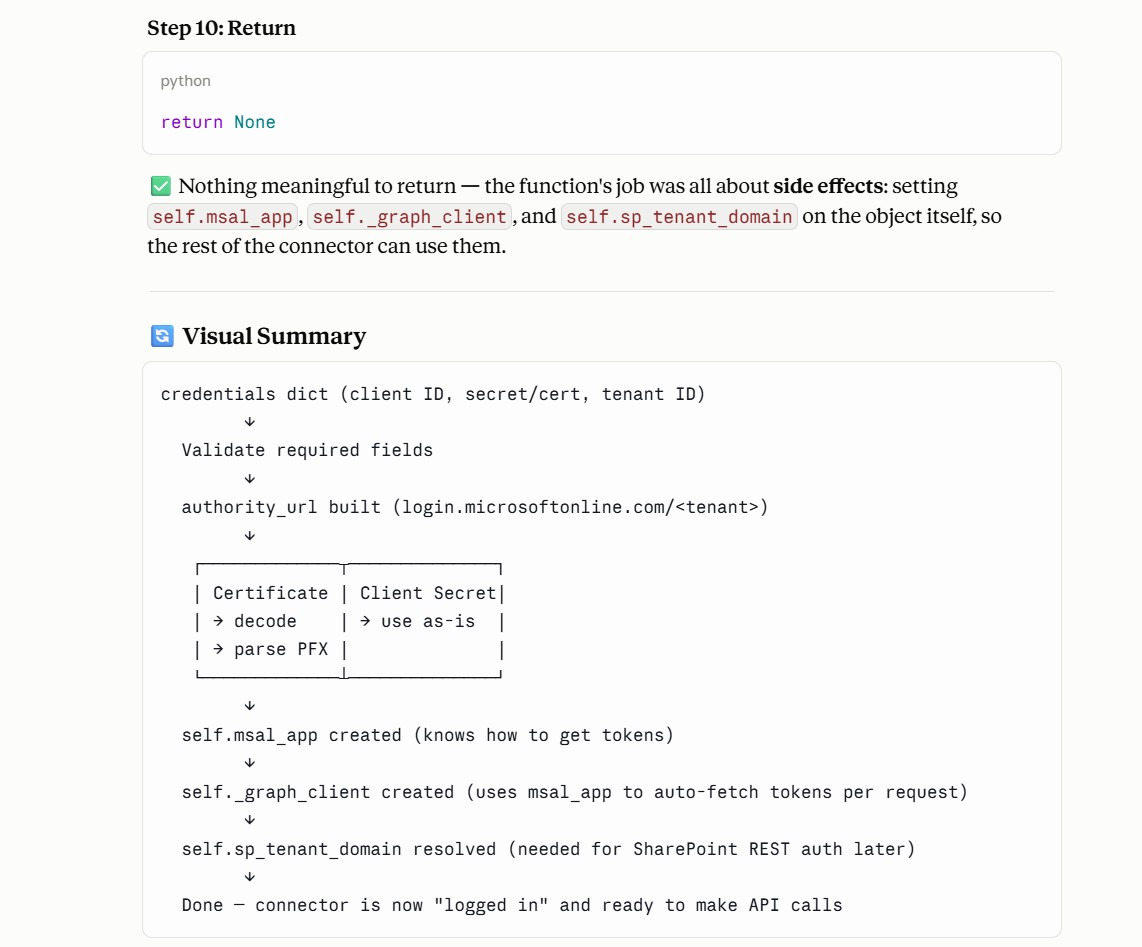
        return None
Your email address will not be published. Required fields are marked *
Comment *
Name *
Email *
Website
Save my name, email, and website in this browser for the next time I comment.